
Introduction
Cyber security compliance means meeting the security requirements that apply to your business under relevant laws, regulations, industry standards, or contractual obligations. It involves more than having security tools in place—it also requires documented policies, access controls, employee training, risk assessments, monitoring, and evidence that these controls are working.
The growing cost of cyber threats makes compliance increasingly important. Global cybercrime costs are expected to reach nearly $11.9 trillion annually, while around 85% of organizations plan to increase their cybersecurity budgets to strengthen protection and keep pace with evolving security regulations.
A clear Cyber Security Compliance checklist helps businesses identify applicable requirements, protect sensitive data, close security gaps, prepare for audits, and maintain compliance over time.
This guide covers the essential controls and practices businesses should review regularly.
Key Takeaways
- Cyber security compliance means meeting applicable security, legal, regulatory, and contractual requirements.
- Compliance requires more than security tools; businesses also need documented policies, procedures, and evidence.
- A strong compliance program should cover access control, data protection, employee training, risk management, monitoring, backups, and incident response.
- Businesses should identify which regulations, standards, and security frameworks apply to their industry and data.
What Is Cyber Security Compliance?
Cyber security compliance means following the laws, regulations, industry standards, and contractual security requirements that apply to a business. It helps organizations protect sensitive data, reduce security risks, and demonstrate that required security controls are properly implemented and documented.
Depending on the business, cyber security compliance may involve:
- Risk assessments to identify and address security gaps.
- Access controls and MFA to protect systems and sensitive information.
- Data protection and encryption for information at rest and in transit.
- Employee security training to reduce human-related risks.
- Monitoring and logging to detect and investigate suspicious activity.
- Incident response and backups to support recovery after a security incident.
- Documentation and evidence to demonstrate compliance during reviews or audits.
The specific requirements vary based on factors such as the industry, location, type of data handled, customers, and contractual obligations.
Is Cyber Security Compliance the Same as Cybersecurity?
No. Cybersecurity and cyber security compliance are related, but they are not the same. Cybersecurity focuses on protecting systems, networks, applications, and data from threats, while compliance focuses on meeting specific legal, regulatory, industry, or contractual requirements.
For example, a business may use firewalls, endpoint protection, encryption, and threat monitoring as part of its cybersecurity strategy. However, it may still have compliance gaps if it cannot document required security controls, employee training, risk assessments, or access reviews.
Cybersecurity |
Cyber Security Compliance |
Focuses on preventing and responding to threats |
Focuses on meeting defined requirements |
Protects systems, networks, and data |
Demonstrates that required controls are implemented |
Uses security technologies and processes |
Requires policies, documentation, and evidence |
Changes based on the threat landscape |
Depends on applicable laws, standards, and contracts |
In simple terms, cybersecurity protects the business, while compliance helps prove that the business is meeting its required security obligations. A strong compliance program should therefore support, rather than replace, an organization’s broader cybersecurity strategy.
Why Is Cyber Security Compliance Important?
Cyber security compliance helps businesses protect sensitive data, reduce security risks, meet applicable requirements, and demonstrate that effective security controls are in place. It also gives organizations a structured way to identify weaknesses and improve their overall cybersecurity posture.
Key benefits include:
- Protects sensitive data: Helps safeguard customer, employee, financial, and business information.
- Reduces security risks: Identifies vulnerabilities and compliance gaps before they become serious problems.
- Meets regulatory requirements: Helps businesses follow applicable cybersecurity regulations, industry standards, and contractual obligations.
- Supports audit readiness: Maintains policies, records, and evidence needed for a compliance audit.
- Builds customer trust: Demonstrates that the business takes data protection and security seriously.
- Improves security practices: Encourages regular risk assessments, security testing, monitoring, and remediation.
For businesses, compliance should not be treated as a one-time requirement. It should be part of an ongoing cybersecurity risk management and security improvement process.
What Types of Data Does Cyber Security Compliance Protect?
Cyber security compliance helps businesses protect sensitive data from cyber threats, unauthorized access, and data breaches. While the specific requirements vary by industry, most compliance frameworks focus on securing the following types of information:
1):- Personally Identifiable Information (PII)
PII includes names, email addresses, phone numbers, government-issued IDs, and other personal information that can identify an individual.
2):- Protected Health Information (PHI)
PHI includes medical records, prescriptions, insurance details, and other patient information that healthcare organizations must protect.
3):- Financial and Payment Data
This includes credit card details, bank account information, payment records, and billing data used in financial transactions.
4):- Business and Employee Data
Businesses must also secure employee records, payroll information, contracts, intellectual property, and other confidential company data.
Is Cyber Security Compliance Mandatory for Every Business?
No, cyber security compliance is not universally mandatory for every business. Compliance requirements depend on factors such as the industry, location, type of data handled, customers, contracts, and applicable laws or regulations.
For example, a healthcare organization may need to follow HIPAA requirements, while a business processing payment cards may need to meet PCI DSS requirements. A company working with certain U.S. Department of Defense contracts may also have CMMC requirements.
Businesses should determine:
- What data they collect and store, such as health, payment, personal, or confidential business data.
- Which laws and regulations apply to their operations and locations.
- Which industry standards or compliance frameworks customers or contracts require.
- What security controls and documentation are needed to demonstrate compliance.
Even when a specific regulation does not apply, maintaining strong cybersecurity practices can help reduce risks and protect business and customer data.
What Cyber Security Compliance Standards and Regulations Apply?
The right cyber security compliance requirements depend on your industry, location, data, customers, and contractual obligations. Common regulations, standards, and compliance frameworks include:
Regulation or Framework |
Commonly Relevant To |
Healthcare organizations handling protected health information |
|
Companies that handle, store, or send credit card information |
|
Service providers that need to demonstrate controls over customer data |
|
Organizations building a formal information security management system |
|
Organizations using a structured framework to manage cybersecurity risk |
|
CMMC |
Certain organizations working with U.S. Department of Defense contracts |
Organizations subject to EU data protection requirements |
|
CCPA/CPRA |
Businesses subject to California privacy requirements |
These should not be treated as universal requirements. Some are regulations or laws, while others are security standards or frameworks. A business may need to follow one or several of them based on its specific obligations.
Before choosing a compliance framework, identify the data you handle, applicable regulations, contractual requirements, and cyber security risks. This helps ensure that your compliance efforts focus on the requirements that actually apply to your organization.
What Should Be Included in a Cyber Security Compliance Checklist?
A cyber security compliance checklist helps businesses protect sensitive data, reduce cyber risks, and meet industry regulations by following proven security best practices. It provides a structured approach to identifying vulnerabilities, strengthening security controls, and maintaining ongoing compliance.
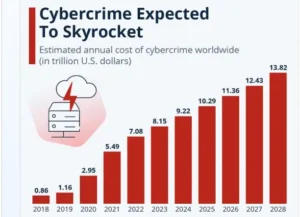
The need for a compliance checklist has never been greater. Nearly 43% of cyberattacks target small businesses, while global cybercrime costs are projected to reach almost $24 trillion in the coming years. Following the checklist below can help your business improve security, reduce the risk of data breaches, and support long-term business continuity.
1. Identify Applicable Requirements
Determine which laws, regulations, industry standards, and contractual requirements apply to your business. Document the specific controls and obligations you need to meet.
2. Identify and Classify Sensitive Data
Know what sensitive information you collect, store, process, and share. Apply the proper security measures and categorize data according to its sensitivity.
3. Perform a Cybersecurity Risk Assessment
Identify security threats, vulnerabilities, and compliance gaps. Prioritize risks based on their potential impact on systems, data, and business operations.
4. Create and Update Security Policies
Maintain documented policies for access control, data protection, password management, incident response, acceptable use, and other relevant security practices.
5. Implement MFA and Access Controls
Use multifactor authentication (MFA) and least-privilege access to limit who can access sensitive systems and information. Review user permissions regularly.
6. Secure Networks and Endpoints
Protect business networks, servers, computers, and mobile devices with appropriate security controls such as firewalls, endpoint protection, secure configurations, and network monitoring.
7. Patch and Update Systems
Apply security patches and software updates promptly. Maintain records showing that critical systems and applications are regularly updated.
8. Encrypt Sensitive Data
Use appropriate encryption to protect sensitive information during storage and transmission, especially when required by applicable compliance requirements.
9. Train Employees
Provide regular security awareness training covering phishing, passwords, social engineering, data handling, and incident reporting. Keep records of completed training.
10. Monitor Systems and Maintain Logs
Monitor important systems and maintain appropriate audit trails and security logs. Regular monitoring can help detect unauthorized access and suspicious activity.
11. Manage Third-Party Risks
Assess vendors and service providers that handle business systems or sensitive data. Review their security practices, contracts, compliance requirements, and risk exposure.
12. Prepare Incident Response Procedures
Create and regularly test an incident response plan that defines how the business will detect, report, contain, investigate, and recover from security incidents.
13. Back Up and Test Recovery Systems
Maintain secure, tested backups of critical data. Regular recovery testing helps confirm that systems and information can be restored after an incident.
14. Conduct Security Testing
Use vulnerability assessments, security audits, penetration testing, or other appropriate testing methods to identify weaknesses in security controls.
15. Collect Compliance Evidence
Maintain evidence such as policies, risk assessments, access reviews, training records, vulnerability reports, logs, backup tests, and incident response exercises.
16. Review and Audit Controls Regularly
Conduct periodic compliance audits and security reviews to identify gaps, document findings, assign responsibility, and track remediation until issues are resolved.
What Evidence Is Needed for Cyber Security Compliance?
Compliance evidence is the documentation and records that show your required security controls are implemented and working. During a compliance review or audit, businesses may need to provide evidence that their policies, processes, and technical controls are being followed.
Common examples include:
- Security policies and procedures — Documented rules for protecting systems and data.
- Risk assessments — Records of identified risks, their impact, and remediation efforts.
- Access review records — Proof that user permissions are reviewed and updated.
- MFA and security configurations — Records showing required security controls are enabled.
- Employee training records — Evidence that employees completed security awareness training.
- Vulnerability and patch reports — Documentation of identified vulnerabilities and remediation.
- System and security logs — Audit trails showing system activity and security events.
- Incident response records — Results from incident exercises, investigations, and response activities.
- Backup and recovery test results — Evidence that critical data can be restored.
- Vendor assessments — Records showing that third-party security risks have been reviewed.
Keep compliance evidence organized, current, and easy to retrieve. Strong documentation can make audits more efficient and help identify security gaps before they become larger compliance problems.
How Do You Maintain Continuous Cyber Security Compliance?
Businesses maintain cyber security compliance by continuously assessing risks, monitoring security controls, documenting evidence, testing processes, and fixing identified gaps. Compliance should be an ongoing cycle rather than something handled only before an audit.
A simple continuous compliance cycle is:
Identify → Assess → Implement → Monitor → Document → Test → Remediate → Review
To maintain compliance over time:
- Review requirements: Check for changes to applicable laws, regulations, standards, and contracts.
- Monitor security controls: Verify that access controls, MFA, encryption, backups, and other safeguards remain effective.
- Maintain documentation: Keep policies, procedures, logs, assessments, and compliance evidence up to date.
- Test regularly: Conduct security assessments, vulnerability scans, recovery tests, and incident response exercises.
- Track remediation: Assign owners to compliance gaps and monitor them until they are resolved.
- Review access: Regularly remove unnecessary accounts and permissions, especially when employees change roles or leave.
- Conduct periodic audits: Use internal reviews or external assessments to verify that controls continue to meet requirements.
This approach helps businesses stay audit-ready, reduce compliance gaps, and adapt their security program as business operations and cyber threats change.
What Are the Most Common Cyber Security Compliance Mistakes?
Businesses often fall out of compliance because they treat it as a one-time project instead of an ongoing process. Common cyber security compliance mistakes include:
- Not identifying applicable requirements: Following a framework without first determining which laws, regulations, or contracts actually apply.
- Outdated security policies: Having policies that no longer reflect current systems, risks, or business operations.
- Poor access management: Giving users unnecessary privileges or failing to review accounts regularly.
- Missing compliance evidence: Having security controls in place but lacking documentation to prove they are working.
- Ignoring third-party risks: Failing to assess vendors that access sensitive data or critical systems.
- Inadequate employee training: Providing security training once and never reinforcing it.
- Untested incident response: Having an incident response plan but never testing whether it works.
- Skipping regular reviews: Failing to monitor security controls and address new vulnerabilities or compliance gaps.
Avoiding these mistakes helps businesses maintain stronger security controls, improve audit readiness, and reduce the risk of costly compliance failures.
How Often Should Cyber Security Compliance Be Reviewed?
Cyber security compliance should be reviewed regularly, not only when an audit is approaching. The right frequency depends on the applicable requirements, business risks, and changes to systems or operations.
Businesses should consider reviewing their compliance program:
- At least annually as part of a formal security and compliance review.
- Quarterly for important controls such as user access, vulnerabilities, backups, and security logs.
- After major changes such as new software, systems, vendors, locations, or business processes.
- After a security incident to identify what failed and what controls need improvement.
- When requirements change to determine whether new regulatory or contractual obligations apply.
Regular reviews help businesses identify compliance gaps, maintain accurate documentation, and keep security controls aligned with current risks and requirements.
Also Read: What Are Managed IT Services and How Do They Work?
FAQ’s
Q1):- How often should businesses conduct compliance audits?
Ans:- Businesses should conduct cyber security compliance audits regularly, including internal reviews throughout the year and third-party assessments annually or based on industry requirements.
Q2):- What happens if a business fails to meet compliance requirements?
Ans:- Failure to meet cyber security compliance requirements can result in financial penalties, legal action, reputational damage, data breaches, and loss of customer trust.
Q3):- How can managed IT services help with cyber security compliance?
Ans:- Managed IT services help businesses maintain cyber security compliance through continuous monitoring, security updates, risk assessments, compliance reporting, and proactive cybersecurity management.
Q4):- Is cyber security compliance mandatory for small businesses?
Ans:- Yes, cyber security compliance may be mandatory for small businesses depending on their industry, location, and the type of customer or financial data they handle.
Conclusion
Cyber security compliance is essential for protecting businesses from cyber threats, data breaches, and regulatory risks. By following a proper cyber security compliance checklist, organizations can secure sensitive data, reduce vulnerabilities, and improve their overall security posture.
Regular risk assessments, strong access controls, employee training, and continuous monitoring all play a key role in maintaining long-term compliance and cybersecurity protection.
Techproc is a trusted IT company in New Jersey that helps businesses strengthen cyber security compliance through IT managed services, cyber security solutions, and proactive IT support.